ISO 27001 Certification Process at Good Việt Nam
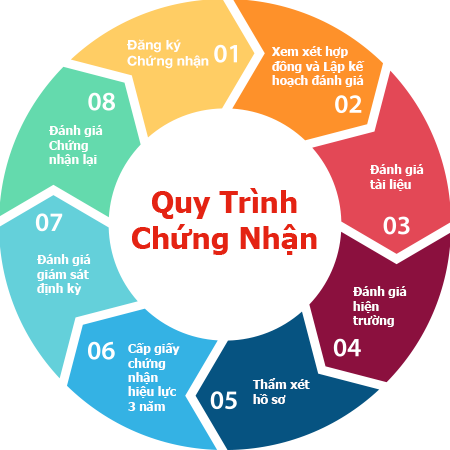
The ISO 27001 certification process by a certification organization follows the steps below. These steps ensure objective certification that meets the standard’s requirements.
Step 1: Customer Information Exchange
The purpose of exchanging information between the certification organization and the customer is to ensure agreement on previously discussed details, ensuring the certification assessment aligns with the standard’s and customer’s requirements. Information exchanged includes:
– Basic certification requirements.
– Certification procedure steps.
– Applicable standards.
– Estimated costs.
– Work plan and schedule.
Step 2: Preliminary Assessment
The business submits to the certification organization: Documents and records related to the implementation of ISO 27001 standards.
The certification organization assigns experts in the relevant field to assess the actual status of ISO 27001 documents, identifying weaknesses in documentation and the practical application of the ISO 27001 system.
After the preliminary assessment, experts must highlight issues with documentation and practical implementation that need correction, allowing the business to address them promptly. This preliminary assessment is highly beneficial as it serves as a guide for the formal assessment.
Step 3: Formal Assessment and On-Site Verification
– The assessment team conducts on-site verification, reviewing the compliance of documents with reality and recommending corrections for any non-conformities.
– During the on-site certification audit, the effectiveness of the ISO 27001 system is evaluated.
– The business’s role is to demonstrate the practical application of ISO 27001 procedures and programs.
– At the end of the on-site audit, the assessment team holds a closing meeting where the business can provide feedback on the findings.
Step 4: Customer Receives ISO 27001 Certificate
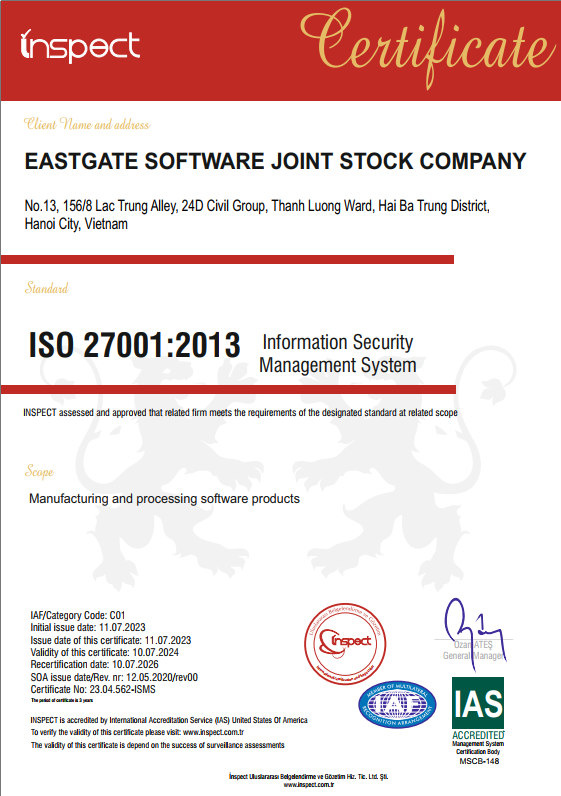
The business receives the ISO 27001 certificate if all documents align with reality and all non-conformities have been satisfactorily addressed, as confirmed by the lead assessor.
Note: The ISO 27001 certificate is valid for 3 years, with mandatory annual surveillance assessments.
Why Choose ISO 27001 Certification Services at Good Việt Nam
Choosing GOOD VIỆT NAM ensures customers receive high-quality services tailored to their business needs. Specifically:
✅ GOOD Việt Nam is an organization with over 10 years of experience in standardization.
✅ GOODVN has assisted hundreds of businesses, including international clients, in achieving ISO 27001 certification.
✅ GOODVN has experts in information technology who understand customers’ operations.
✅ Expands export opportunities to international markets for businesses.
GOODVN’s ISO 27001 consulting and implementation services include:
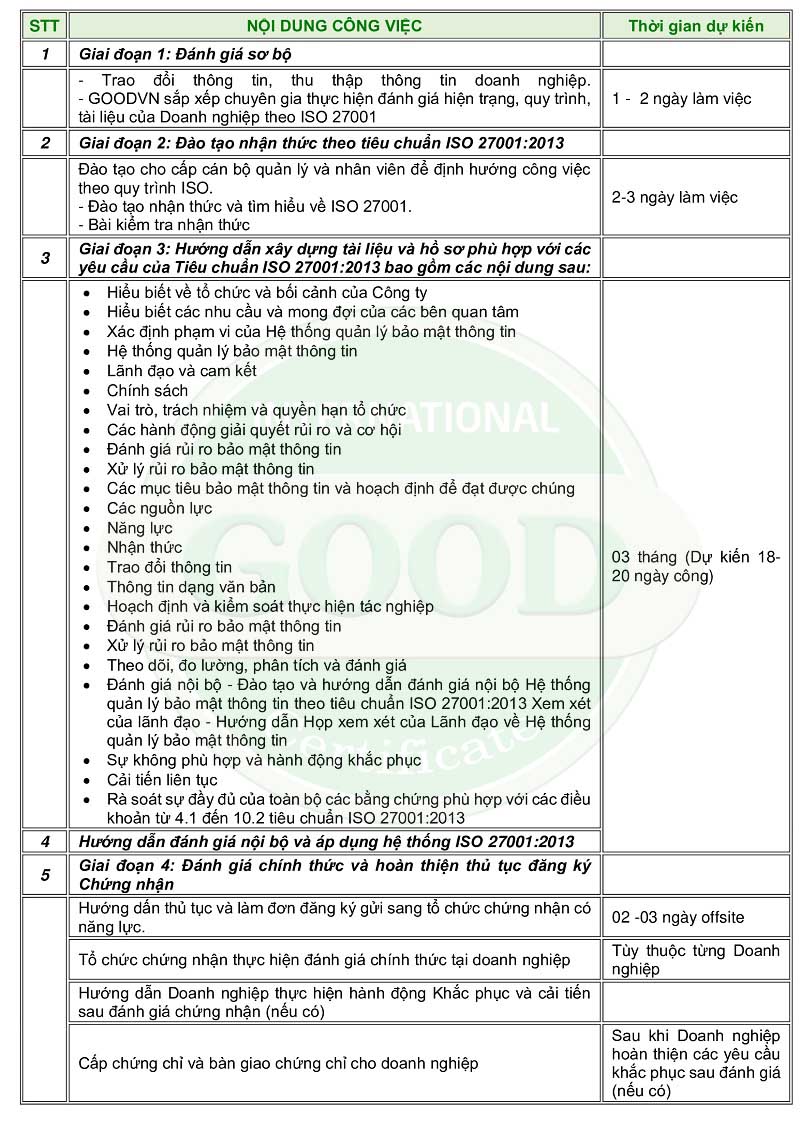
- A network of branches across all three regions ensures responsiveness to business needs anytime, anywhere.
- GOOD Việt Nam guarantees reasonable implementation timelines tailored to each customer.
- Customers of Good Việt Nam always receive the most competitive costs.
- A team of highly competent experts with over 10 years of experience, providing dedicated and professional consulting support.
Frequently Asked Questions About ISO 27001 Certification
WHO APPLIES ISO 27001?
ISO 27001 applies to all organizations, regardless of size or location. This voluntary standard focuses on establishing, maintaining, and improving an information security management system.
COST OF ISO 27001 CERTIFICATION?
ISO 27001:2022 is a complex standard with numerous requirements, and its implementation and certification process is more intricate than other standards. Therefore, the cost of achieving ISO 27001 certification is higher than other standards.
Certification costs are only part of the expenses for implementing and adopting ISO 27001. Businesses should also budget for the following costs:
1. Costs for Implementing ISO 27001 Standards
These are costs for training, initiating process development per ISO standards, and applying them within the business to ensure quality control.
2. Certification Costs for ISO 27001 by the Certification Organization
These are costs for the certification assessment process conducted by a certification organization. Certification costs typically vary depending on the scope, location, and size of the business.
GOODVN will assist businesses in calculating the costs of implementing and certifying ISO 27001 based on the information provided by the business.
GOODVN supports customers in implementing and achieving ISO 27001 certification. Contact us now for the best support!
CONTACT: 0945.001.005 – 024.2231.5555
WE ARE HERE TO SERVE YOU!